MeetSecuritain—Built by Cloudain for Modern Cloud Securitysecuritain.com
We understand the concern of putting AI in front of company data and business systems without a clear way to control it. That's why we're here: to help you adopt AI with confidence, not compromise. AI becomes more valuable when it can access company knowledge, connect with business systems, and perform useful actions, so we help you put clear controls around data access, model usage, agent permissions, human approval, and monitoring—moving you from experimental tools to controlled business solutions.
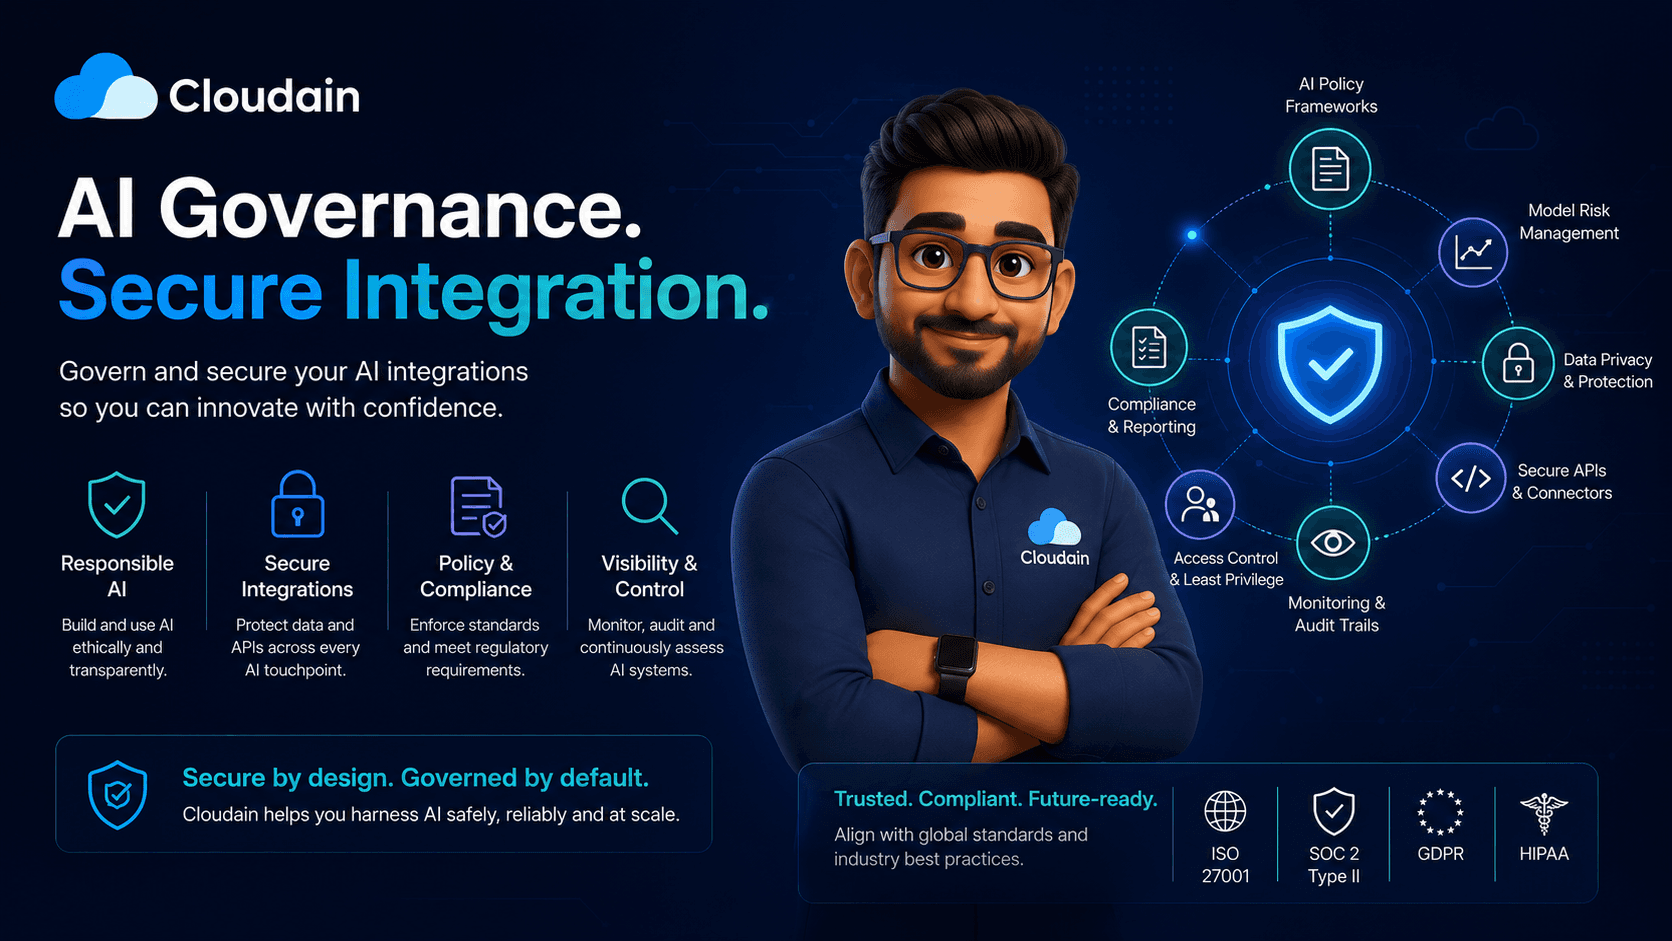
An AI assistant may search internal documents, retrieve customer information, call APIs, or initiate workflow actions. Without the right controls, it can receive more access than it needs or expose information to the wrong user. Cloudain places controlled boundaries around every connection.
From security architecture and secure integration to data protection, agent security, guardrails, and a practical governance framework.
Design clear security boundaries around how models, apps, users, data, and systems interact.
Connect applications to Bedrock, OpenAI, Anthropic, Azure OpenAI, and other approved platforms.
Control what information AI systems can retrieve, process, and return.
Agents receive limited, task-specific permissions—not broad access to business systems.
Controls around how AI apps accept requests and generate responses.
Practical rules for adopting and operating AI—built to be applied, not shelved.
The goal isn’t to claim every incorrect response can be eliminated—it’s to reduce risk, detect failures, and respond safely when information is insufficient. Cloudain controls how AI apps accept requests and generate responses, from prompt-injection defense to sensitive-data filtering and escalation.
We work with your existing cloud environment and standards rather than forcing a separate platform for every AI initiative.
From internal assistants and customer chatbots to regulated apps, SaaS products, agentic workflows, and enterprise adoption.
Protect access to policies, technical docs, project information, and internal knowledge.
Control what a chatbot can provide, protect customer data, and add staff escalation.
Stronger identity, data protection, audit, and human-review controls for AI workflows.
Tenant isolation, usage metering, model access, data boundaries, and secure AI APIs.
Restrict agent permissions, validate tool inputs, and require approval for key actions.
Shared security and governance standards for many teams, apps, and model providers.
A practical foundation—assessment, architecture, framework, implementation, evaluation, monitoring, and handover.
A review of existing AI apps, integrations, data flows, access controls, and operational risks.
A practical design of apps, models, knowledge, APIs, identities, boundaries, and monitoring.
Where information originates, is processed, which providers receive it, and how access is controlled.
Policies, responsibilities, approval requirements, and release controls teams can actually apply.
AI gateway, model connections, identity, retrieval security, agent permissions, guardrails, monitoring.
Tests for response quality, data access, restricted actions, failure handling, and policy compliance.
Dashboards and alerts for usage, failures, model activity, agent actions, cost, and security events.
Architecture docs, operational procedures, control guidance, and knowledge transfer.
Scope and timing are based on the number of applications, data sources, providers, integrations, and risk requirements—not a fixed timeline.
Review a proposed or existing AI solution and identify security, privacy, and governance gaps.
Design and build the security and integration foundation for an assistant, RAG app, or agent workflow.
Reusable policies, patterns, approval controls, and monitoring for many AI initiatives.
Assess data exposure, excessive permissions, insecure APIs, weak retrieval, and unmanaged model usage.
We work across AI applications, cloud-native development, APIs, identity, security, and compliance architecture—and build our own platforms too. That gives us practical experience with the challenges that appear when AI moves beyond a demonstration and begins accessing real information and systems.
Whether you’re launching an AI assistant, connecting models to an existing application, or introducing agent-based workflows, Cloudain helps define and implement the security and governance foundation.
Data, access & actions bounded
Usage, cost & policy visible
Secure and operable over time
Cloudain implements technical and operational controls aligned with your organization’s security, privacy, and governance requirements. Regulatory or legal compliance depends on the complete organizational, contractual, and operating environment.
